Fraud Alert: No OTP, No Fake Call—Hackers Exploiting Fintech Systems To Divert Crores
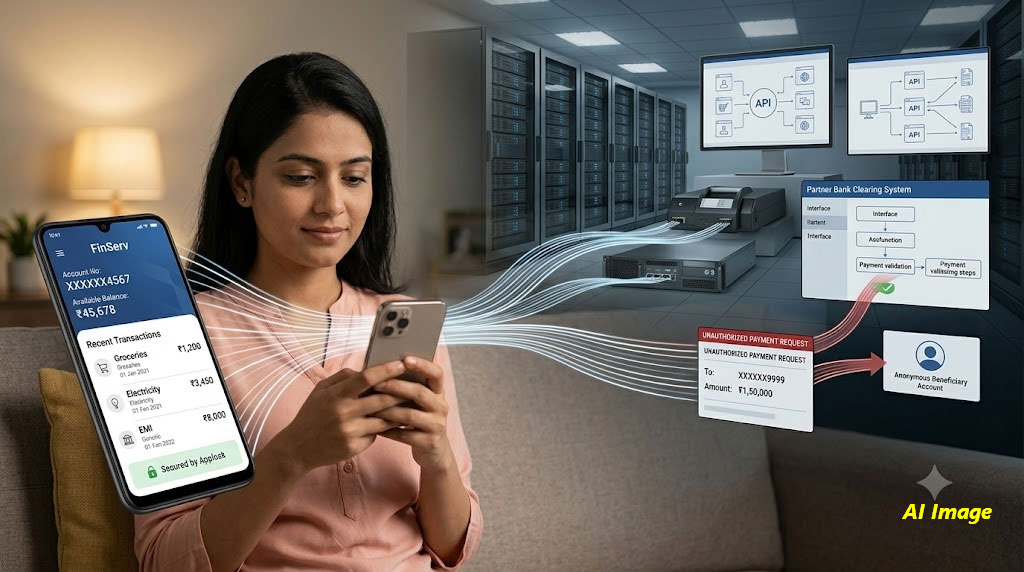
Picture this. You completed your know-your-customer (KYC) formalities, submitted all required documents, your loan is approved, and the lender is following every step before releasing the loan funds. But what if a cybercriminal finds a way around all those checks and simply instructs the payment system to send the funds to an account he controls?
That is the danger flagged in a serious warning from the Indian computer emergency response team (CERT-In), working with the computer security incident response team for finance sector (CSIRT-Fin). The agencies have spotted several attack campaigns targeting financial institutions (FIs) like non-banking financial companies (NBFCs), digital lending platforms, fintech firms, payment service providers and digital wallet operators.
What makes this unsettling is that the criminals may not need to touch a customer’s bank account at all. They don’t even have to trick anyone into revealing a one-time password (OTP). Instead, they go after the information technology (IT) systems that the FI use to approve and send money. Once inside the system, they can exploit weak spots to trigger unauthorised payouts, slipping past the very checks meant to prevent fraud.
For financial customers, the lesson is clear. The safety of your money is not dependent only on how carefully you guard your passwords, but also on how strongly the institutions holding your money guard their own systems.
How Criminals Can Get Past the Checks
Financial institutions use application programming interfaces, or APIs, to connect their systems to banks, payment gateways, lending platforms and other service providers. Think of an API as a digital channel. One system uses it to ask another for information, or to tell it to do something, such as money transfer.
Modern financial services cannot work without these links. But if criminals get hold of valid API credentials, or find a flaw in the system, they can misuse the same channels that genuine businesses depend on.
CERT-In has found that attackers break into internet-facing applications, exposed APIs and privileged access points. They then steal the credentials used to connect with payment gateways, aggregators or partner banks. In some cases, they can send fund-transfer instructions directly through the bank’s or NBFC’s own approved infrastructure, so the activity appears to be from a trusted source.
That lets them sidestep the usual safeguards: loan account file creation, KYC checks, approval procedures, beneficiary verification, balance checks and transaction limits.
The criminals may also submit dummy loan or transaction reference numbers that match no genuine record. They then trigger several high-value transfers through banking channels such as IMPS (immediate payment service) and NEFT (national electronic funds transfer), sending the money to accounts run by their accomplices or to mule accounts controlled by them.
These are the same mule bank accounts we hear so much about, used to receive and move funds stolen in cybercrimes. The money from these accounts is often withdrawn or transferred within minutes, making it much harder to recover. In other words, you can trace how the proceeds of the crime are being routed, but then there may not be any money left in the account you reached. This is because it may have been physically withdrawn or transferred to another account or accounts.
The Weak Spots Hackers Exploit
The CERT-In warning lists several possible ways hackers can access FI systems. These include vulnerable online applications, outdated software components, unused or poorly secured APIs and remote services that lack multi-factor authentication (MFA).
Criminals may also dig out API keys and passwords left lying in source code, configuration files or databases. Some credentials stay valid for a long time which gives attackers plenty of room to misuse them once stolen.
CERT-In also points to another risk: tampering with software development repositories through forged code changes. If malicious code creeps into a company’s development process, weaknesses can be built in before an application even goes live.
Once inside, attackers can plant hidden backdoors, study payment databases and map the company’s links with banks or payment providers. CERT-In has also flagged the deletion or manipulation of system logs and interference with endpoint detection and response tools. Both make it harder for investigators to piece together what happened.
The agency says recent incidents suggest the gap between the first break-in and the fraudulent transfers is getting shorter. It also warns of possible use of artificial intelligence (AI)-assisted attack tools and large numbers of automated scripts. That does not mean every incident involves AI, but it shows how fast criminals can move once they find a way in.
What This Means for You
When a lender’s or payment provider’s IT systems are compromised, the damage can go well beyond the money lost from the FI’s own accounts. Depending on the incident, customers could face disruption in payments, rise in disputed transactions or leakage of personal and financial information.
Let us be clear about what the warning does not say. It does not mean every bank, NBFC, UPI app, wallet or fintech platform has been breached. Nor does it mean every customer is at immediate risk. What it does show is why you should choose financial platforms carefully and stay alert to anything unexpected.
This is also completely different from the familiar scams in which fraudsters phone you posing as bank officials or send links to steal your OTP. Here, the target is the financial institutions’ own systems. So even a customer who follows every sensible password rule could still be affected if the institution’s infrastructure is compromised.
That is why personal precautions must go hand in hand with a close look at the services you use.
How To Protect Yourself
1.Choose regulated, established providers. Before taking a digital loan or using a wallet, check who runs it, whether it is regulated, and whether it is linked to a legitimate bank or regulated lender. A slick-looking app or website proves nothing when it comes to money transactions.
2.Never share OTPs, PINs or passwords. If a caller claims to be from a bank, NBFC or payment company, do not hand over any confidential details. And never download and install remote-access or screen-sharing apps because someone offers to fix a payment problem.
3.Turn on transaction alerts. Enable SMS, email or app notifications for transfers, card payments and other activities. Check them promptly, especially those involving new beneficiaries, unfamiliar transfers or payments you did not initiate or were not expecting.
4.Check your accounts regularly. Don’t wait for the monthly statement. Look at recent transactions in the official bank or finance app. Report unfamiliar debits, unexpected credits, or duplicate transactions in writing to your FI at once.
5.Stick to official apps and websites. Download financial apps only from trusted sources, and verify who is behind them. Stay away from APK files sent on messaging apps, links in unsolicited messages and websites that mimic genuine lenders or payment companies.
6.Secure your phone and email. Use a strong screen lock, keep your phone’s software and apps updated, and delete apps you no longer need. Switch on MFA for your email wherever possible, as it is often used to reset passwords and receive sensitive account alerts.
7.Take unexpected money seriously. If unexplained money lands in your account, don’t pass it on, and don’t follow a stranger’s instructions to send it back through a separate payment. Call your bank or FI on its official number and ask it to verify the transaction.
8.Act fast if something looks wrong. Contact your bank, FI or service provider through official channels and ask for the disputed transaction to be investigated. Report suspected cyber financial fraud promptly by calling 1930 and filing a complaint on the national cybercrime reporting portal (NCRP) at cybercrime.gov.in. Keep transaction IDs, messages, screenshots and complaint references. Don’t delete evidence and don’t pay anyone who promises guaranteed recovery.
Financial Companies Must Shut the Back Door
CERT-In’s recommendations make one thing plain: customer awareness alone cannot stop this kind of attack. Financial institutions must lock every route through which money can leave their systems.
That means stronger authentication, removing unused APIs, changing credentials regularly, restricting access to production servers and checking every payout against a genuine, approved transaction. FIs should also enforce transaction limits at the payment-system level, verify beneficiaries independently, require a second approval for fund movements and watch for unusual transfers in real time.
They must also match their own records against bank and payment-provider statements fast enough to catch transfers that don’t correspond to legitimate instructions. Well-protected logs and regular security testing are equally important, both for spotting intrusions and for preserving evidence.
The takeaway for customers is simple. Digital payments may take seconds, but the systems behind them need strong controls at every stage. Cybercriminals are increasingly hunting for weaknesses in the institutions that move money, not just in the people who use them.
You cannot secure a lender’s API or inspect its payment infrastructure yourself. But you can choose your providers with care, keep an eye on your accounts and report suspicious transactions without delay. When your money moves through a system you do not control, vigilance remains your first line of defence.
Stay Alert, Stay Safe!